


Good Morning:
Yes, the photo above was made with AI. But sometimes, life will imitate art, and this is one of those time.
On July 22, unbeknownst to me until the other day, the IRS approved the 501(c)(3) status of the #GreekChorusFoundation, which means that all contributions to the foundation—including those that have already happened—are now tax deductible.
Then, last week on #DogShirtTV, the estimable Anna Bower lamented that a certain MAGA lawyer was disgracing membership in what she termed, the “Dyed Red Hair Club.” I had, at the time, never heard of the Dyed Red Hair Club, but I immediately thought that this would make challenge for our new status.
So, here’s my challenge to you all: The foundation currently has three separate projects ongoing: Operation Taya, Operation Battery, and Operation Slava. On October 31, Taya’s next tuition payment is due, and we have committed to giving Slava’s family a second payment. If we meet those fundraising targets, I will join the illustrious membership of the Dyed Red Hair Club.
Make it happen, folks:
Last Tuesday on #DogShirtTV, the estimable Anastasiia Lapatina told us about the Russians’ latest attack on her leisure time, the estimable Holly Berkley Fletcher reported on an ex-evangelical comedy festival, and the estimable Andrew Steele helped us continue to brainstorm arch disruption techniques:
Wednesday on #DogShirtTV, memoirs of a gringo, the estimable Windsor Mann:
Thursday on #DogShirtTV, the estimable Holly Berkley Fletcher brought on the extremely estimable Kristin Du Mez to tell us about her latest book, on the history of American evangelical femininity:
Friday on #DogShirtTV, the estimable Anna Bower and the estimable Molly Roberts came on to talk about the Grand Conspiracy—and the Dyed Red Hair Club:
Monday on #DogShirtTV, the estimable Holly Berkley Fletcher wanted to talk about slug sex. I don’t know, it’s a revolution, I guess:
Yesterday on #DogShirtTV, I showed off my staircase plan and the estimable John Hawkinson brought up some interesting issues related to ballot security:
Recently On Lawfare
Compiled by the estimable Sarah Willrich
Why We’re Suing the State Department Over International Agreements
Scott R. Anderson discusses Lawfare’s decision to sue the State Department over its failure to release documentation of its international agreements. Anderson breaks down what the lawsuit alleges, why Lawfare decided the suit was necessary, recent litigation developments, and what comes next.
This collapse of the disclosure system mandated by Congress presents some very specific problems for Lawfare. Over the past two years, Lawfare has covered and analyzed countless aspects of the Trump administration’s foreign policy that hinge on international agreements or non-binding instruments, from the deportation of migrants to third countries to new deals with trading partners to arrangements with Ukraine regarding its natural resources. But because of the Trump administration’s non-compliance, we’ve been forced to do so without the documents themselves or an understanding of their purported legal basis. This undoubtedly makes it more difficult for us to fulfill our stated mission of better educating the public on matters of national security law and policy. It also directly undermines Congress’s stated legislative purpose of promoting “greater understanding of the use of international accords as a foreign policy tool.”
Homeland Security 25 Years Later: Time to Rethink and Rebuild?
As part of Lawfare’s Sept. 11 essay collection, former Secretary of Homeland Security Jeh Johnson argues that now, 25 years after 9/11 transformed how the U.S. approaches homeland security, it is time to substantially reorganize it. Johnson proposes streamlining the many agencies and departments that make up the patchwork system into a single Cabinet-level agency that combines law enforcement, counterterrorism, cybersecurity, and aviation security while keeping certain immigration and disaster response functions separate.
The politically volatile immigration (or, as some would say, anti-immigration) mission has overwhelmed DHS. The component of our government originally intended to “keep us safe” is viewed in many communities primarily as a pariah, an enemy of the people, a heartless deportation machine to be reviled for family separation, masked men snatching people off the streets at night, and the killing of innocent civilians for which there has been no apparent accountability. Mayors and city councils in blue cities don’t want to work with DHS at all, to the detriment of public safety.
Twenty-five years after 9/11, it’s time to rethink homeland security.
The Changing Face of the Department of Homeland Security
Paul Rosenzweig traces how the Department of Homeland Security (DHS) evolved from a border security and counterterrorism initiative to monitoring domestic threats and finally to a sprawling immigration apparatus. Rosenzweig argues that, though each shift was often justifiable, together they gradually resulted in a DHS that has lost sight of its original mission and its remaining public support.
So the Department of Homeland Security had to change to focus on a threat now embedded in, well, the homeland. But that brought new challenges. Where, initially, the Department of Homeland Security had looked at the conduct of foreigners, now a more substantial fraction of those under scrutiny were American citizens or lawful residents. The swing of the pendulum now began to have a real “bite” for everyday Americans.
The most salient problem in this change of focus was distinguishing the fine line between speech that is political and speech that is intended to incite violence and radicalization. America’s commitment to free speech makes regulation of violent rhetoric particularly difficult. As the Department of Homeland Security turned its focus inward, it, of necessity, began to redraw that boundary.
Ordinary Origins: How 9/11 Built Today’s Immigration Enforcement Machine
Chinmayi Sharma analyzes the origins of automated immigration enforcement, arguing that today’s immigration system has its origins in data-sharing approaches first conceived after 9/11. Sharma explains how systems once designed to prevent intelligence oversights have since quietly expanded into a massive ecosystem of data on millions of Americans.
And where government systems did not contain enough information, agencies bought it. The Privacy Act governs systems of records operated by or on behalf of an agency, but federal officials treated commercial data resellers’ databases as outside that rule because the vendors served multiple customers. By 2006, 91 percent of reported federal reseller use was for law enforcement or counterterrorism, and ICE was already DHS’s largest customer; agencies commonly bought address and vehicle information—where people were. The scale advantage was dramatic: in one 2005 test, a TSA contractor sent roughly 240,000 passenger names to three commercial providers and received more than 100 million records back. Interoperability could connect government silos; the commercial market could fill the gaps between them.
Justice in the 9/11 Case is Long Overdue
Michel Paradis and Nick Lewin discuss the plea agreements the 9/11 defendants detained in Guantanamo Bay reached with prosecutors, which the government later backed out of. Paradis and Lewin argue that the agreements were the only chance at justice for both the defendants and 9/11 victim families, and they urge the Supreme Court to review whether the government can withdraw from the agreement.
Without these plea deals, no trial is anywhere on the horizon. It has been a quarter-century since the 9/11 attacks. And even if the military commissions can ultimately limp to the starting line of a trial, immense challenges remain. There is a very real chance that the years of motions and appeals that lie ahead will surpass the years of life these rapidly aging men have left to live. That presents a significant risk that these men will die without a final judgment of conviction—leaving them presumed innocent, at least in the eyes of the law, and denying families some sense of finality and closure.
The Unexpected Emergence of the EU as a U.S. Counterterrorism Partner
Kenneth Propp reviews how, following 9/11, the U.S. and EU formed a series of agreements that altered precedent for transatlantic counterterrorism cooperation and international law. Together, Propp explains, the agreements greatly expanded U.S.-EU data sharing, created the expectation of mutual aid, and solidified the EU as a legal body to negotiate with.
The EU saw these twin agreements as a way of making Brussels more relevant in the transatlantic policy conversation on law enforcement and counterterrorism issues. The United States government agreed with this ambition, as was noted to the Senate: “[T]he U.S.-EU Agreements will enable the strengthening of an emerging institutional relationship on law enforcement matters between the United States and the European Union, during a period when the EU is actively harmonizing national criminal law procedures and methods of international cooperation.”
Through periodic joint reviews of the agreements, the United States, EU institutions and EU member states jointly assess past performance and discuss common implementation problems. While criminal law in Europe remains largely a member state affair, the EU over the years has come to play a genuine role in addressing transatlantic law enforcement challenges including terrorism.
9/11’s Legacy of Torture
Natalie K. Orpett discusses the torture of detainees following 9/11 and why it still matters today. She explains why existing legal measures have failed to provide justice for victims and accountability for perpetrators. Though the initial shock has faded, Orpett argues that the United States’s failure to confront its legacy of torture exposes a fundamental failure of law—and that the same “pretense of legality” is now enabling abuses against immigrants and other detainees today.
The consequence is that those who perpetrated and enabled the torture have suffered almost no repercussions, and those who were victims of torture have seen no real justice. All of which is itself a clear signal that the law failed. What is the law for, if not to punish wrongdoers and provide redress to those whom they injured?
Of course, that doesn’t help the case for those who think of 9/11 and its aftermath as a historical artifact. To them, I say this: when a legal system has systematically failed to metabolize lawless, unconscionable government conduct, there is something wrong with that system. If we don’t figure out what, how will we combat lawless government conduct in the future—or now?
The 25th Anniversary of the 2001 AUMF
Jack Goldsmith asserts that the 2001 Authorization for the Use of Military Force (AUMF) has outlived its usefulness. He explains that the gradual expansion of the president’s Article II authority has eroded the practical need for an AUMF. At this point, Goldsmith argues, reforming the 2001 AUMF would have little effect. Only Congress can meaningfully rein in the president’s war authorities going forward.
Article II as interpreted by the executive branch thus provides everything a president needs to use force against any threatening terrorist organization, including all of the al Qaeda-associated and successor forces for which the AUMF is now invoked. Put another way, if Congress abrogated the 2001 AUMF tomorrow, the president would have all of the authority he needs under Article II to continue using force against all current terrorist threats around the globe.
Presidents will surely continue to invoke the 2001 AUMF against legacy terrorist organizations for path-dependent and prudential reasons. But they don’t need to, for the legacy organizations, or for future threatening terrorists or terrorist organizations that rise up.
Misunderstanding 9/11
Daniel Byman identifies five analytic mistakes regarding 9/11: the U.S. failed to recognize 9/11 as an exceptional event rather than a harbinger of worse attacks to come; officials underestimated how much sustained counterterrorism pressure could diminish the threat; they failed to appreciate how unusual pre-9/11 Afghanistan was as a terrorist safe haven; they overlooked deep divisions among jihadist groups; and they overestimated the U.S.’s ability to reshape political systems in the Middle East.
These mistakes point toward a more sustainable strategy. Policymakers should avoid hyping the threat: Terrorism is real, but not all terrorists pose the same threat. Some are unskilled, and most are focused on local enemies, not the United States. To address the threat as it exists, counterterrorism capabilities should be consistently resourced because expertise, intelligence relationships, and community trust cannot be surged quickly when danger rises.
The United States should also exploit terrorist weaknesses, especially jihadist infighting, and keep pressure on genuine havens through intelligence, cooperation with local governments, support for local forces, and limited strikes when necessary. But not every haven is another 1990s Afghanistan; that was the exception, not the rule.
25 Years of Mass Surveillance is Enough
Cindy Cohn and Bruce Schneier weigh the costs of 25 years of expanding mass surveillance since 9/11 and argue that it’s time to reverse course. Cohn and Schneier explain that the increasing surveillance of every American by the government and, increasingly, private companies is both practically harmful for society and legally unsound. They suggest that Congress should consider comprehensive changes to privacy law.
More generally, ubiquitous surveillance carries a real societal cost. The chilling effects are real and pervasive, and they tend to fall hardest on the most marginalized members of society. Moreover, social progress requires the ability to experiment in secret. It’s hard to imagine a society progressing morally to the point of accepting and legalizing things like marijuana use or gay marriage if the earliest signs of that shift are snuffed out because of overzealous surveillance.
Terrorism’s Second Act
Peter Beck, Seamus Hughes, and Camden Carmichael discuss terrorist recidivism and what can be done to prevent it. They warn that without a comprehensive plan, more repeat attacks are likely to happen. The authors argue that commitment to extreme ideologies is often worsened by social isolation, which efforts to prevent recidivism can inadvertently reinforce.
Research has shown that extremists disengage from violence as their social role and sense of identity evolve. As extremists, their beliefs are intertwined with an urge to act, and taking action is part of who they are. Someone who takes pride in doing everything and anything for a cause doesn’t want to be accused of sitting on the sidelines. But when former extremists find a different identity—through education or employment opportunities, new relationships, or social circles—it provides an opening, allowing them to self-justify disengaging: ‘Why carry out a terrorist attack when I just got a new girlfriend or hired for a job with great coworkers?’
The opposite is true when strong stigma exists against a former extremist, because it reinforces the role of a terrorist as their place in society. When relationships and opportunities spurn someone, they’re likely to shift back to what they found comfort in before, even when it’s as extreme as supporting a violent ideology.
America’s Driver’s License Breach is a National Security Disaster
In the latest edition of the Seriously Risky Business cybersecurity newsletter, Tom Uren discusses a new dark web service that was selling access to identification documents such as U.S. driver’s licenses, the military’s disabling of ad identifiers to prevent service members from being tracked, white hat hacks, and more.
Identity verification services are necessary to help to prevent fraud, but are also a point of vulnerability when security is poorly done. The sheer volume of sensitive data these services handle means that they should be subject to strict regulation and oversight.
We’re realists here at Seriously Risky Business, though, and recognise that there is no chance of swift government action. In the short term, we can only hope that significant financial consequences will help encourage these firms to shore up their security. Law firms are already lining up class action suits against IDScan, but a little federal government attention from the FTC wouldn’t be unwelcome either.
Laundering Federal Election Interference in the Midterms
Julia Curlee argues that the Trump administration’s recent claims about Chinese election interference are part of its broader efforts to manipulate intelligence to discredit election results. Curlee describes how the administration’s recent claims that voting machines are vulnerable could be used to later justify blocking unwelcome election results. She recommends steps the pro-democracy coalition can take to push back against such claims by elevating the role of civil society, preparing lawyers, and providing information about the voting process.
First, the administration will use official documents, including declassified intelligence assessments and the DHS letterhead, to claim the underlying vulnerability constitutes an ongoing threat. Why the alleged manipulation hurts the president’s party and only helps his opponents will go unexplained. It will not attempt to prove that any votes were changed. No such evidence exists, but the accusation itself is the point, and the alleged machine vulnerability cannot be remediated before Election Day.
No amount of auditing, and no use of the SAVE database, can prove the negative that no fraud occurred. In place of evidence, the administration will borrow the credibility of the CIA, DHS, and FBI to declare that specific counties’ voting machines have been “compromised.” The right-wing media ecosystem has already kicked into gear, claiming the DHS memo confirms that previous elections were stolen.
Why We Opted Not to Work at the AI Labs
Bharat Chandar and Kevin Frazier warn about the dual brain drain of experts leaving academia to join the artificial intelligence (AI) industry and the brain wane of students joining AI firms instead of pursuing further studies. Chandar and Frazier argue that having a robust population of independent experts is critical to regulating and understanding AI and advocate for adjusting incentives to maintain that talent outside the labs.
But without a healthy ecosystem of external experts, regulators may become increasingly reliant on industry researchers to draft responsive regulations. A review of the visitors log to the White House, for example, would reveal that visits from AI CEOs and calls from staffers with ongoing connections to industry stakeholders tend to coincide with major policy shifts. Congressional hearings have also tended to include significant industry participation. Under the status quo, the public may have to form its understanding of the technology based on company talking points, with a resultant breakdown in trust over the technology’s promise and peril. And, in the longer term, the next generation of AI experts may be smaller than an alternative world in which higher education institutions have the resources and personnel necessary to train students about the latest and greatest tech.
Podcasts
On Scaling Laws, Christina Lee joins Kevin Frazier to discuss Lee’s forthcoming article, “Beyond Algorithmic Disgorgement: Remedying Algorithmic Harms.” They consider what algorithmic disgorgement is, why the Federal Trade Commission first used it, why its expansion matters, and whether alternate approaches could work.
On Rational Security, Scott R. Anderson celebrates the fifth anniversary of Rational Security 2.0 with co-hosts emeriti Shane Harris, Quinta Jurecic, and myself. We sit in brutal judgment of this year’s Hot Take Takedown pitches provided by Julia Curlee, Michael Feinberg, and Molly Roberts on topics ranging from the President’s Daily Brief to the Bourne movies.
On Friday’s Lawfare Daily, Katherine Pompilio speaks with five members of the Lawfare team—Julia Curlee, Michael Feinberg, Natalie Orpett, Loren Voss, and me—to talk about how 9/11 shaped the U.S. national security apparatus and our careers.
On Tuesday’s Lawfare Daily, Tyler McBrien sits down with Zoe Kurland and Terence O’Rourke to discuss “A Whole Other Country,” a podcast series hosted and produced by Kurland that tells the story of a secessionist movement in the mid-90s called the “Republic of Texas.”
Videos
On Lawfare Live, I sit down with Molly Roberts, Anna Bower, Roger Parloff, Eric Columbus, and Peter Beck to discuss the latest developments in litigation surrounding the Trump administration, including the administration’s attacks on mail voting and more.
Today’s #BeastOfTheDay is the llama, which we honor today for bringing about the headline “Abandoned Llama Not Interested in Being Rescued on Colorado Trail”
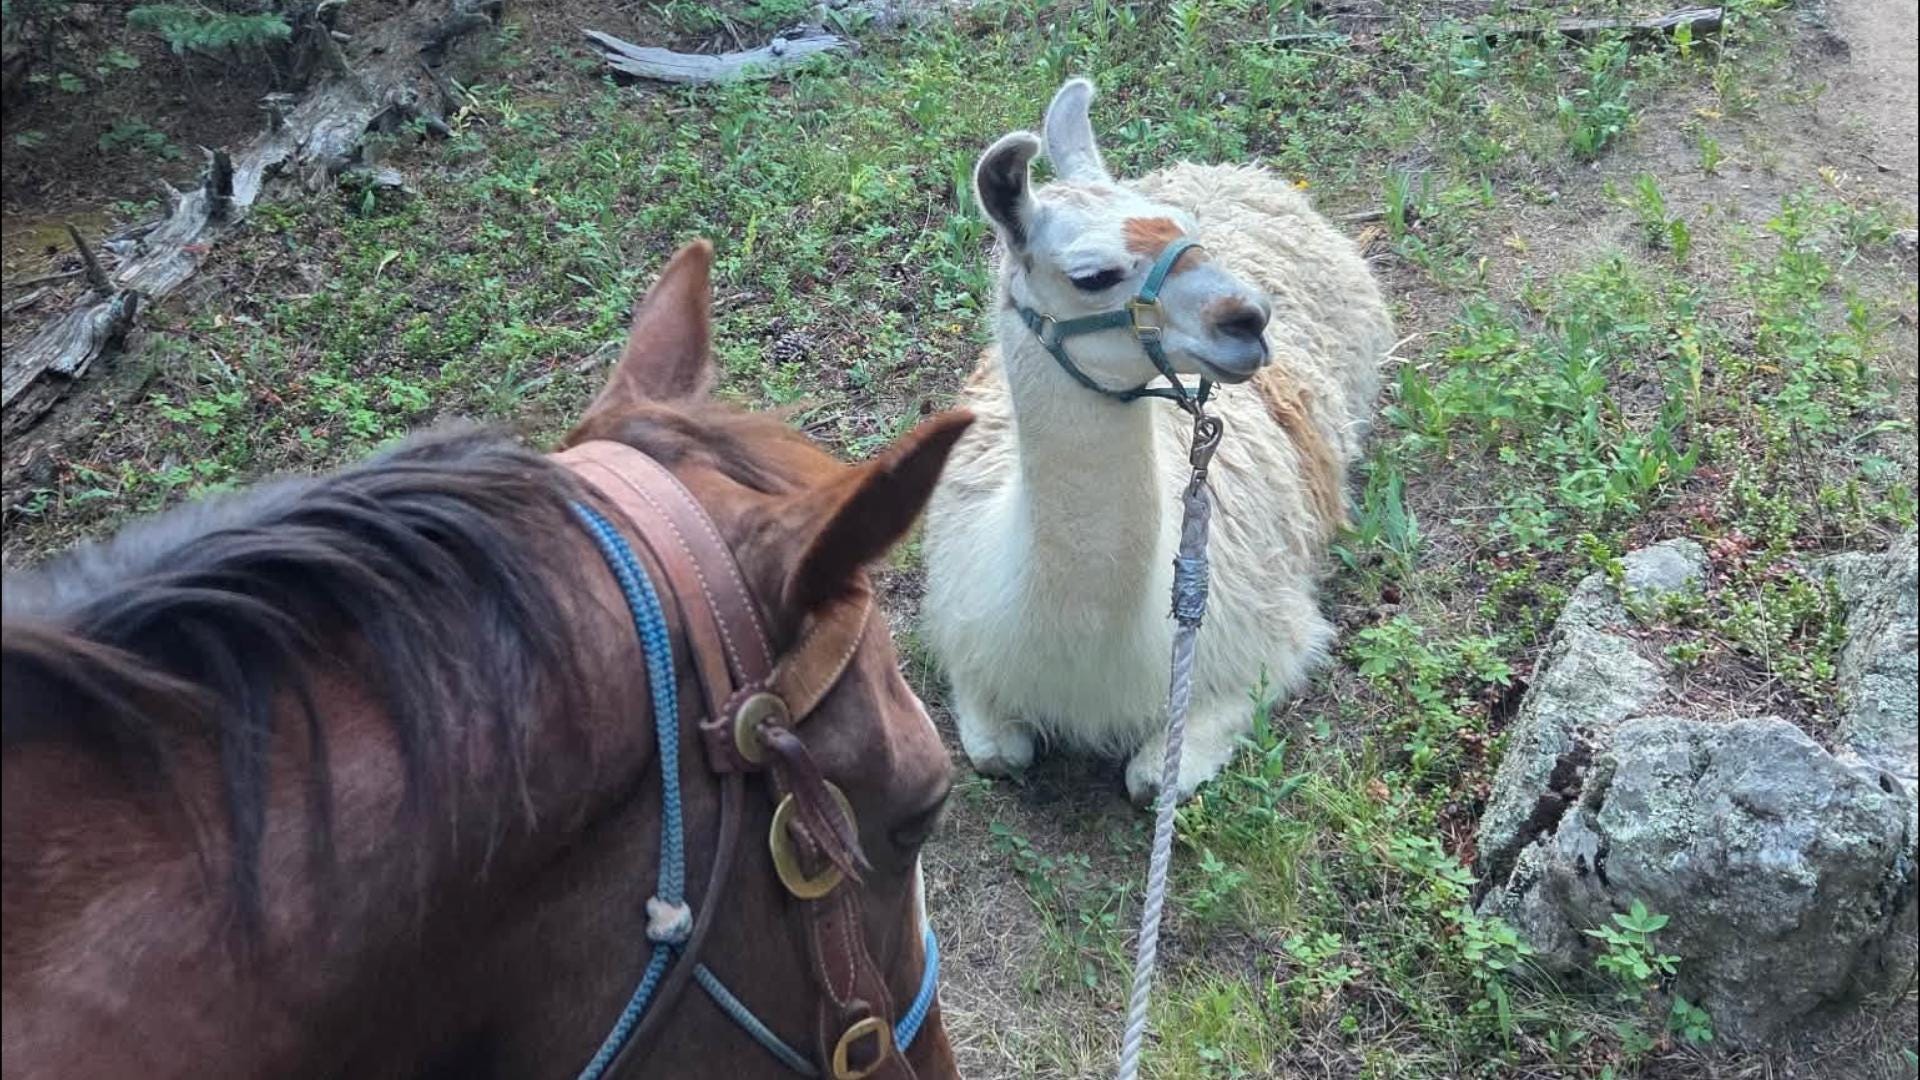
A stubborn llama is back home after being discovered on a Colorado mountain trail.
The Larimer County Sheriff’s Office said its deputies recently responded to a call about an abandoned llama on the Comanche Peak Trail, west of Fort Collins.
After being located resting comfortably in a wooded area where she was hitched to a tree, deputies attempted to lead the lounging llama back to civilization.
“The llama was not interested in this plan,” the sheriff’s office said. “They’d get her 30 feet down the trail, then she’d decide it was time for a 45 minute rest.”
Deputies said they tried to coax the llama into the evening, managing to make it over a mile, but the llama again rested. Deputies left the llama with food and water, then returned early the next morning…
“The owners were advised to leave a note or notify law enforcement should the llama stage an impromptu backcountry bivouac in the future.”
In honor of today’s Beast, emulate the llama by peacefully resisting law enforcement, especially if you can arrange to be in the way of one of Trump’s construction projects in the process.
Tell Me Something Interesting
Apropos of the estimable Windsor Mann’s appearance on the show, it occurred to me—EJ Wittes—to wonder exactly how old the term WASP actually is.
Wikipedia credits the earliest known usage to Stetson Kennedy in 1948, citing this 2012 letter to the New York Times on the issue. That’s already older than I would have guessed, but the usage itself suggests a term already circulating. The letter cites Kennedy as saying, “In America, we find the WASPs (White Anglo-Saxon Protestants) ganging up to take their frustrations out on whatever minority group happens to be handy — whether Negro, Catholic, Jewish, Japanese or whatnot,” which sounds to me like a man using a term already in the vernacular and clarifying it as an afterthought for those not in the know.
